CY CyberM365 Security
Microsoft 365 · access map · Teams campaigns

Who can open what in your Microsoft 365?

See it in minutes. Then let the people who shared it close it, right in Teams.

On the map: “Anyone” linksguests nobody remembersfolders still shared with a former contractorfiles open to the whole companylinks created by people who have left

  • Read-only scanner
  • Hosted in France
The access map of a fictional tenant: the red cells are access nobody decided. Or watch Cyber in 80 seconds.
~30 s
to sign in with Microsoft
< 10 min
to the first results
0
file contents read or stored: we keep counts
14
days of full trial, no card
Three situations you may have without knowing

Nobody decided it. It accumulated.

You inherited this tenant. It is not a fault. Your figures will be different. They will not be zero.

Copilot

Copilot breaks nothing. It finds what everyone can already open.

Files open to the whole company, to guests, or to anyone with the link: Copilot answers from all of it. Cleaning up before it is opened to everyone costs far less than after the first "how did you find that?".

A leaver

Disabling an account does not close its shares.

Badge returned, laptop returned, account disabled. Their OneDrive is still shared with two outside addresses, an "Anyone" link still opens the price list, and they still reach a dozen sites. No offboarding checklist has a box for that.

Storage

You may be paying for files nobody opens.

SharePoint storage beyond the included pool is billed every month. Inactive sites, leavers' OneDrives and forgotten archives fill it quietly. Cyber shows the biggest sites and drives, quotas over 90 % and what is safe to archive.

See · Fix · Prove

One scan, three results for your next audit.

Drawn from the read-only scan: no extra Microsoft permission, no file opened.
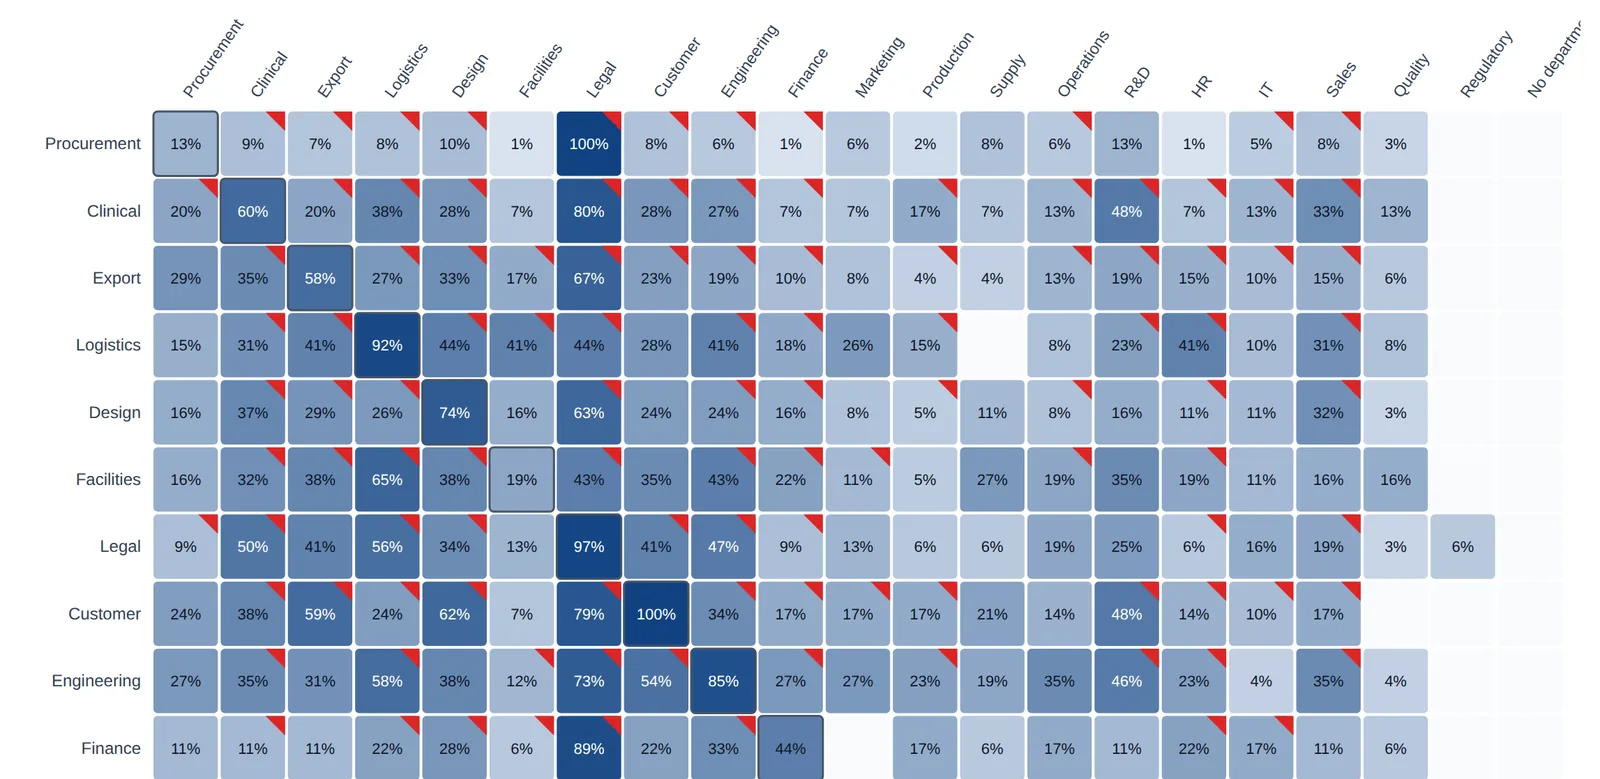
Access map heat grid: share of each department that can open the sites of every other department
Which departments open which departments' sites? Rows: the people of a department. Columns: the sites of a department. The diagonal is normal; the red corners nobody decided. One click on a cell lists the sites.
  • All the real access of one person: the leaver view
  • Where does access leave the company?
  • Sites and Teams nobody uses any more
  • Sites named like sensitive content (payroll, HR, contracts) flagged for every other department, without reading a file or an E5 licence
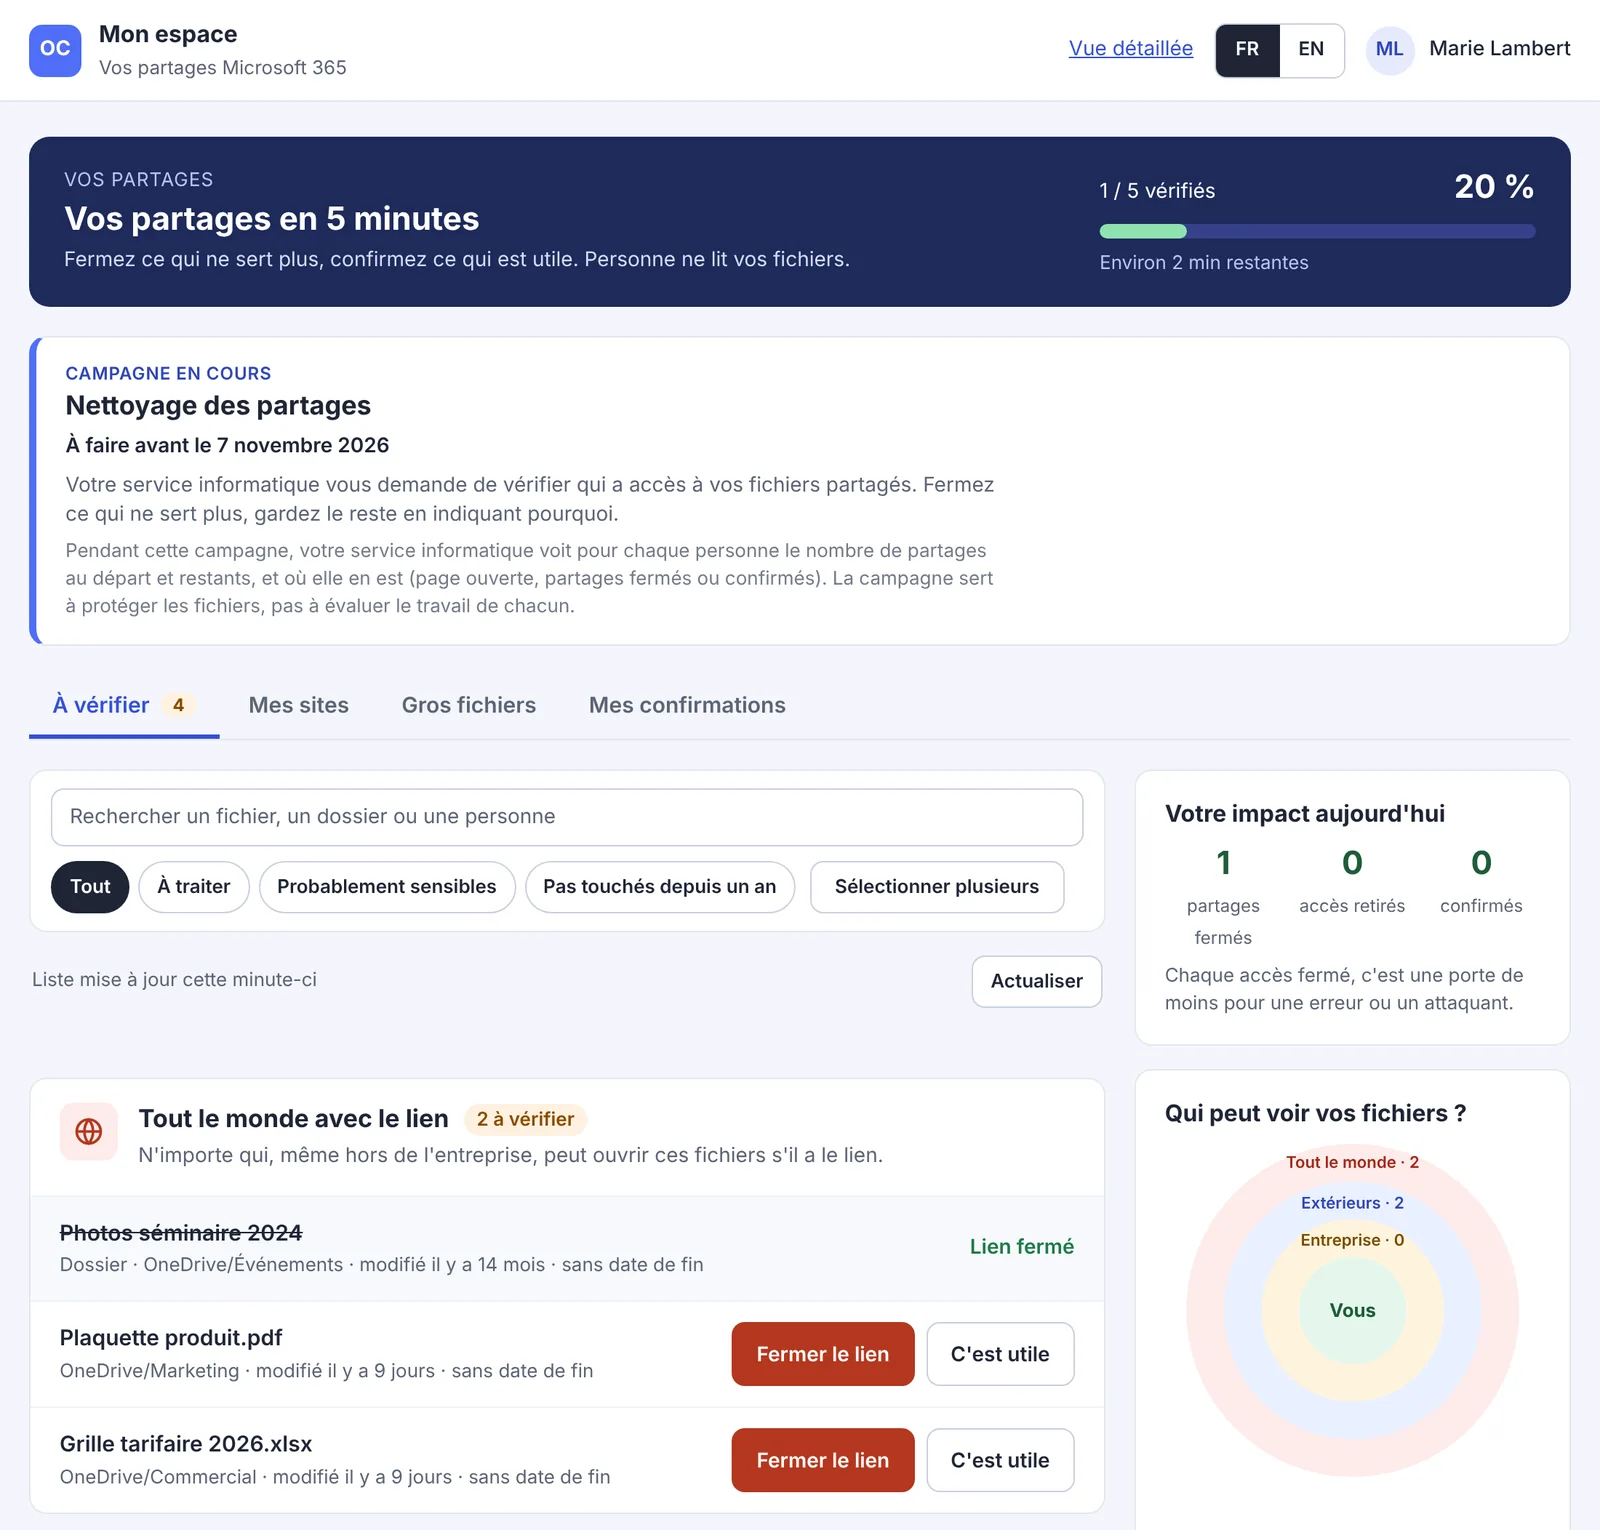
Mon espace: progress 1 of 5 checked, the running campaign and what IT sees, links to close or keep, who can see your files
Mon espace: what the employee sees Their progress, the campaign and its deadline, what IT can and cannot see, then each link with "Close the link" or "It's useful".
  • You pick the sources, the link types, 14 to 35 days, the tone and the language
  • A Teams notification and a chat message; reminders on working hours only
  • Mon espace opens inside Teams: they fix with their own Microsoft rights
  • Olyteck sends, reminds and stops on its own. No ticket, no script, no chasing
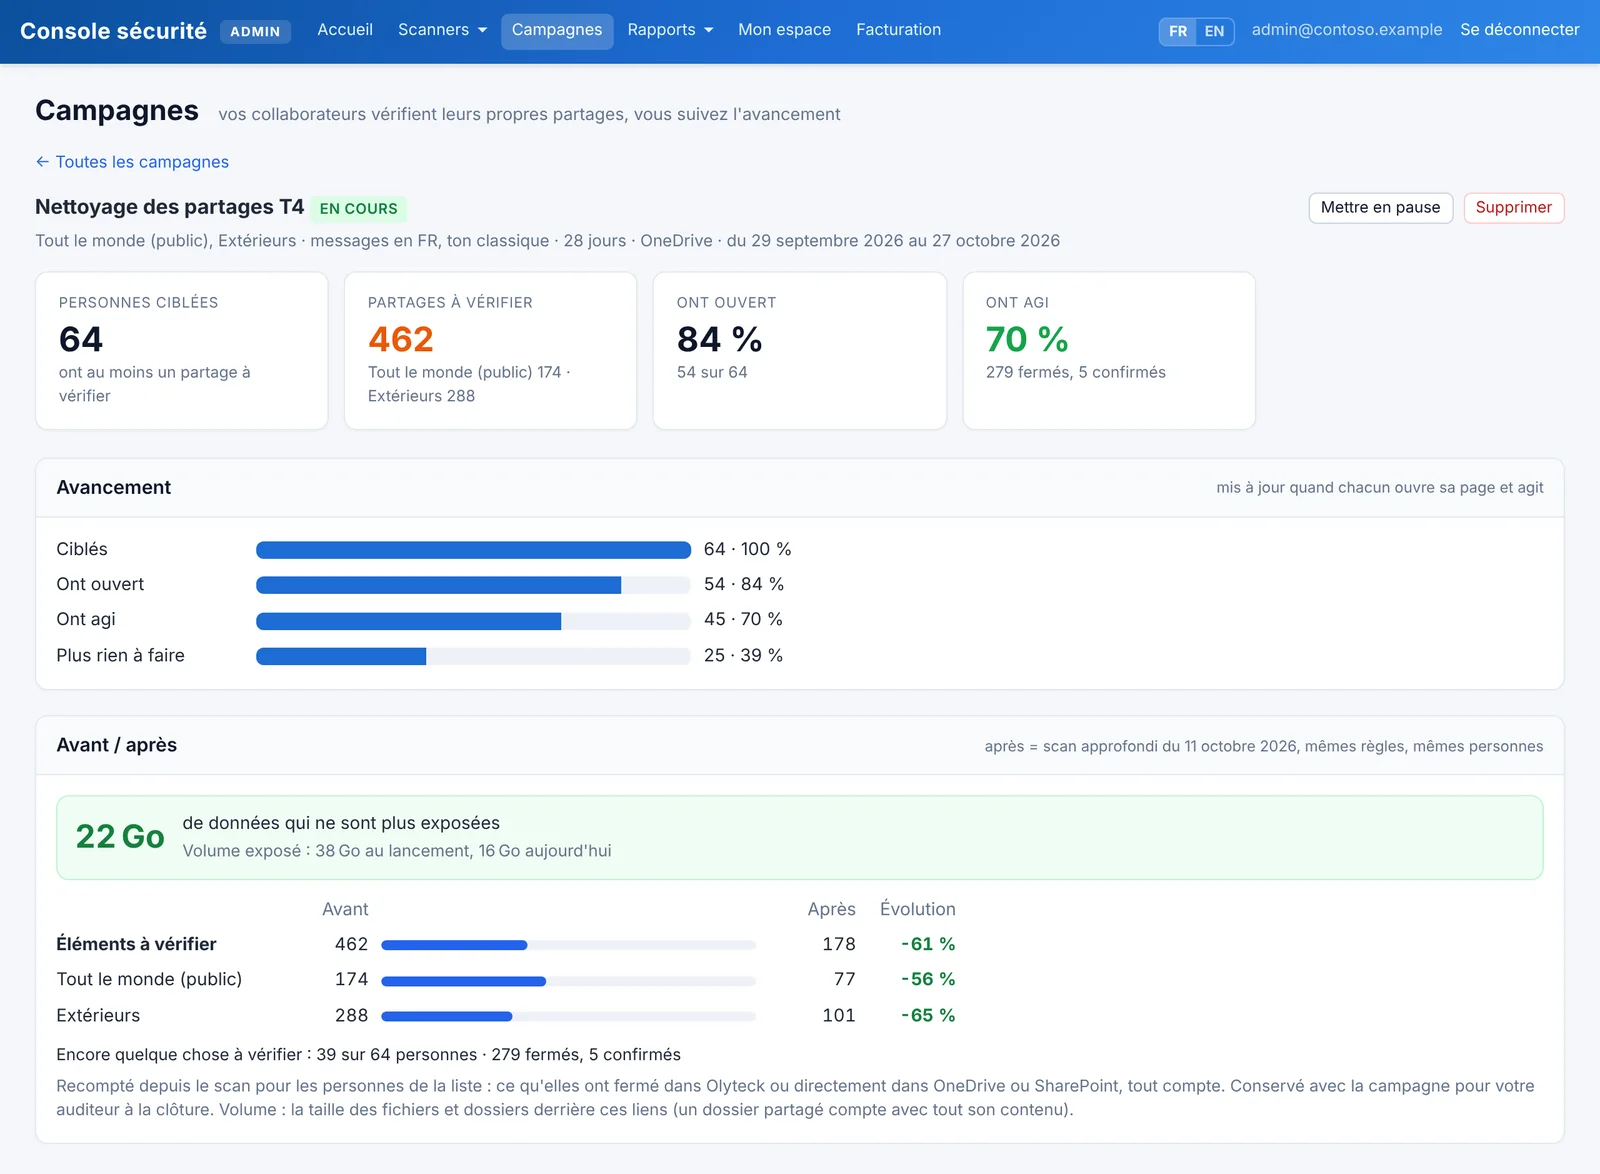
A running campaign in the console: people targeted, shares to check, opened, acted, progress bars and the before / after
What IT sees: who opened, who acted, and the before / after "After" is a new deep scan with the same rules and the same people. It is kept with the campaign for your auditor at close. Figures of a fictional tenant.
  • Targeted, opened, acted, nothing left to do: per campaign and per department, with the before / after and a CSV export.
  • Every accepted access carries a name, a date and a reason, and comes back for review after 12 months
  • NIS2 (Article 21) asks the entities it covers for access control policies and asset management; ISO 27001 calls it an access review (A.5.15, A.5.18). The map, the decisions and the follow-up are the evidence.

Typical situation · fictional tenant · real Olyteck Cyber screens

Scan #1 · value in minutes

Here's what a typical first scan actually surfaces.

The exact shape of the findings the SharePoint and OneDrive scanners produce. Names and figures are examples.

Critical
5 anonymous links on site "Client-X-Shared"
Oldest link created 2022-03-14. No expiry. Default sharing link set to "Anyone".
Warning
OneDrive for alex@acme.com – 312 GB
User licence revoked 2025-11. Account disabled. Drive still holds 312 GB.
Info
Leaver check: 1 person → 14 Teams, 3 sites owned alone, 9 live share links
Person view before the exit interview: every group membership, every site they own alone, every link they created – including the ones shared to their private address. Remove or revoke from one screen; export the rest as the offboarding checklist.
Critical
External guest holds Owner on 4 team sites
partners@vendor.com – last sign-in 2025-09. Still Owner on Finance-Q4, Legal, HR-Docs, Ops.
Show 7 more findings from the same scan
Warning
7 sites above 90% quota · top site 4.2 TB
"Marketing-Archive" at 4.2 TB / 4.5 TB. Projected full in 6 weeks at current growth.
Warning
8 OAuth apps with Mail.ReadWrite · 3 inactive
Three apps not seen in tenant sign-in logs > 90 days. Still consented. Safe to revoke.
Critical
Team "Project-Phoenix" is Public – 412 users can read M&A channel
Visibility set to Public on creation. All org-wide licensed users can join, read channels, and download files – including the M&A-Q4 channel.
Warning
47 Teams have no owner · 8 inactive > 180 days
Original owners offboarded. Nobody can approve new members or archive. Export the list and flag them for archive.
Info
23 M365 Groups eligible for archive · 1.8 TB reclaim
Zero activity > 180 days. No guests. Safe archive candidates. Add to the Archive Queue and export the report for your ops team.
Critical
"Anyone with the link" default is tenant-wide
Org-level default sharing scope is still "Anyone". Every new link inherits it.
Info
3 admins without MFA enforced
Global Admin + SharePoint Admin + Exchange Admin. Conditional access not requiring second factor.

Every finding exports to CSV, links back to the exact SharePoint/OneDrive object, is timestamped for auditor evidence – and has a fix button next to it: revoke the link, remove the member or guest, demote the owner. Read-only until you say otherwise. Run your own scan →

Live in under 10 minutes

Three steps to your map. A fourth, when you decide, to fix it.

From "I just heard about this tool" to "here is who can open what" – typically under 10 minutes to the first results on a standard tenant.

1

Sign in with Microsoft

Standard Microsoft SSO. PKCE, delegated scopes. We never see your password. Takes ~30 seconds.

~30 seconds
2

Grant read-only admin consent

One click by a tenant admin. 19 read-only Graph permissions. You can revoke consent at any time from the Microsoft admin centre and the scanner stops cold.

1 click
3

Deep scans run on our servers

Started for you, in France, with no browser left open. First results in minutes; a large tenant completes in the background. Then every 7, 14 or 30 days, or on demand.

Minutes, then background
4

Fixing and campaigns – when you decide

A separate application with its own consent: it acts as the person who clicks and shows in your own Microsoft audit log. Teams messages go through a third application that reads nothing. Never enable them and the product stays read-only.

Optional · separate consents
What we never store

Your files never leave your tenant.

Most scanners ingest the content. Cyber – M365 Security doesn't. Here are the three classes of data we deliberately do not pull or persist.

✕ File contents

We don't read what's inside your files.

No document bodies, no attachments, no OCR text. The scanner identifies that a file is shared, never what is inside it. Your IP and customer data never enter our database.

✕ Share URLs

We record that a share exists – not the link.

When a SharePoint site has an "Anyone" link, we store the count and severity. We do not store the URL itself. Rogue links can't leak from our database because we never asked for them.

✕ Scanner access tokens

Scanner tokens live in memory for one scan – then are gone.

Held in memory for one scan, then discarded. The optional fixing and Teams connections keep an encrypted token (AES-256-GCM, key outside the database) that you delete by disconnecting them. A copy of our database alone cannot be replayed against your tenant.

Four Microsoft applications, each with one right

Separate apps, separate consents, each one revocable on its own. You can check every grant in Entra under Enterprise applications.

Sign-inIdentifies the person through Microsoft. Nothing else.
Scanner19 read-only permissions. Reads, never writes.
Fixing · optionalCloses a link or removes a member, as the person clicking, with their rights.
Messaging · optionalSends Teams notifications to people who have the Olyteck app. Reads nothing.

Employees involved? Built by a DPO. We give you the CSE information notice and the IT-charter clause. The campaign list (name, e-mail, department, counts, events) is deleted 90 days after the campaign closes. No ranking of people, no file names, no links kept.

The full SAFE-payload rule is codified in our Privacy Policy §3.

The first question every admin asks

"Doesn't Microsoft already do this?"

It shows you settings. Site by site, page by page, across four admin centres that get renamed every year. What it doesn't give a small team is the answer: who can reach what, since when, and what to do about it.

Admin centre: settings

Cyber: consequences, per person, per Team, per link

Pick one person and see every Team, site and sharing link they hold – the leaver check in one filter. Pick one Team and see what is open internally, to guests, or to anyone on the internet. Close it in one click. That is the access review an auditor asks for, done in minutes instead of a week of PowerShell.

Microsoft: four consoles that keep moving

Cyber: one checklist of best practices that stays put

Entra, Purview, Defender, SharePoint admin – tools get renamed, pages move, the guidance is scattered. Cyber keeps the controls that matter in one place, in ISO 27001 and NIS2 vocabulary, readable by an IT team that doesn't have a Microsoft security specialist on staff.

Secure Score: a target you can't reach

Cyber: the score achievable on the licences you pay for

Half the recommendations need a P2 licence you don't have, so 100 % is off the table and the number stops meaning anything. Cyber shows the maximum achievable on your current licences, the points you can win today, and what an upgrade would actually unlock – before you buy it.

Admin centre: one global admin does everything

Cyber: the clean-up goes to the people who shared

Each owner gets their own list in Teams and works through it in Mon espace, with their own rights. You keep the overview and the proof; nobody gets admin rights.

Microsoft shows you the problem. Fixing it stays IT's job. Here, everyone fixes what they shared. Cyber reads your tenant through Microsoft's own read-only Graph permissions and works on Business Basic, Standard and Premium. No P2 required.

What an evaluator said
"Achieving the same level of visibility using native Microsoft capabilities alone can be difficult or, in some cases, not possible."
A corporate security lead at an IT services company, during a formal vendor evaluation of Cyber

See the map of a tenant like yours, in 20 minutes.

We show you the access map, a campaign in Teams and the trace for your auditor. If your Global Admin joins, we run your first scan together and you leave with your own findings.

Pricing

Simple pricing. No surprise paywall.

Three editions, priced by licensed users (up to 100, 300, 600 or 1,000). Your 14-day trial unlocks everything. Annual billing is 2 months free; monthly has no lock-in.

Voir

See who can open what: access map, risks and reports.
from €99/mo
billed annually · up to 100 users, then by size
  • 5 modules included
  • Daily scheduled scans
  • Access map and admin reports
  • 90-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial
Most popular

Corriger

Owners fix their own shares from Teams. IT watches the results.
from €199/mo
billed annually · up to 100 users, then by size
  • 6 modules included
  • Daily scheduled scans
  • Clean-up campaigns in Teams + Mon espace
  • 180-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial

Piloter

All seven modules, unlimited scans, a year of history.
from €299/mo
billed annually · up to 100 users, then by size
  • All 7 security modules
  • Daily scheduled scans
  • Clean-up campaigns in Teams + Mon espace
  • 360-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial

Prices for every size, MSP and Enterprise on the pricing page.

One clean-up, no subscription

The clean-up campaign pack

For a first campaign, before a Copilot rollout, or for a budget line this year: 45 days of Cyber with campaigns, then you decide.

One-off price, licensed Microsoft 365 users, VAT not applicable (art. 293 B du CGI). Over 1,000 users: on quote.

Order a campaign →

Paid by card? We activate your 45 days within one working day and send you the kit.

Common questions

What every IT lead asks before the first scan.

Will my employees think the Teams message is phishing?
It comes from inside your tenant. The message is sent by the Olyteck app your admin installed in your own Teams, it opens a page signed in with Microsoft, and it never asks for anything but the usual Microsoft sign-in. Before launch, announce the campaign from your own management: we give you the text, to be signed by your IT and security leads. No e-mail from an unknown domain asking staff to "fix their shares".
Do we have to inform the works council (CSE)?
In France, usually yes, and we make it easy. A campaign shows each employee their own shares: that is processing of employee data. We give you the CSE information notice and the IT-charter clause. What we keep is minimal: name, e-mail, department, counts and campaign events, deleted 90 days after the campaign closes. No ranking of people, no file names, no links.
What if people don't fix anything?
Expect a minority to do most of the work, and that is enough. Exposure usually sits with a few owners, so the people who act close most of the risk. Reminders stop as soon as someone has nothing left. What remains at the end, IT closes from the console, one click per link.
How long does a campaign take, and how much IT time?
14 to 35 days, chosen at launch. A campaign starts from a deep scan of 7 days or less (one click: "Run now"). Then messages go out on their own, Monday to Friday, 8:30 to 18:30 in your tenant's time zone. IT time: the launch, a look at the funnel, and the remainder at the end.
Is the scanner really read-only? Can it change anything in my tenant?
Yes – and it is not a setting, it is the permission grant. The scanner application holds 19 Microsoft Graph permissions and every one of them is read-only. It has no write permission of any kind, so there is no code path by which a scan can modify your tenant. It is also the only identity that reads your tenant on a schedule, so nothing on a timer can change a file, site, group or setting (the only other scheduled action is sending the Teams reminders of a campaign you launched).

Fixing what we find is a separate application, and it is optional. Revoking a sharing link or removing a group member needs its own Entra registration, consented separately and revocable on its own. If you never enable it, the product cannot modify your tenant at all – every fix button refuses and tells you which permission it would need. When you do enable it, it acts as the person clicking, with that person's own rights, and the action appears in your own Microsoft audit log.

Don't take our word for it: check Enterprise applications → Permissions in your own tenant, or Security Console → Apps & consent in the product, which reads the live grant from Microsoft on every load. Security review brief (PDF) →
What data do you actually store in your database?
Counts, IDs, and severities – not content. For each finding we store the site, person or app it is about (ID and name), the finding type, the severity, and the timestamp. We do not store file contents, share URLs or email bodies, and the scanner's access tokens are never stored. Two exceptions, both about one person's own choices: a share an employee confirms in My space keeps the file name and their reason, and a fix waiting for an approval keeps its file name for up to 30 minutes. The optional fixing and Teams chat connections keep an encrypted refresh token. See Privacy §3 "SAFE payload" for the precise field list. Database is hosted in the EU. Scan history is available and kept for 90, 180 or 360 days depending on your plan (Voir, Corriger, Piloter; Enterprise: as agreed), then deleted; a resolved finding is deleted 180 days after it was resolved (360 on Piloter).
Do I really not need a credit card to start?
Correct. Sign in with Microsoft, grant admin consent, and you're in. The 14-day free trial unlocks all 7 modules – SharePoint, OneDrive, Copilot, Identity, Email security, OAuth apps, Posture – with daily scheduled scans, weekly digest, critical alerts, and saved reports. Nothing rolls over to a paid plan automatically. When the trial ends, the product switches to read-only until you pick a plan.
How long does a scan actually take?
5–15 minutes for most SMB tenants. Heavily-loaded tenants (500+ SharePoint sites) can run longer. The scanner is rate-limited to respect Microsoft Graph throttling and always yields to your users – no impact on production. You can run up to 20 on-demand scans per day during the trial.
Show 7 more questions
Can I share findings with my accountant or external auditor?
Yes. Any scan can be snapshotted to a saved executive report – cover page, trend chart, top findings, auditable timestamp. Share externally via a signed URL with your own expiry, or export findings as CSV for evidence attachments. No re-query needed from the auditor's side.
Will this disrupt my users during a scan?
No end-user impact. All calls go to Microsoft Graph application endpoints using the tenant's own admin consent – not to users' mailboxes or OneDrives. Users won't see a prompt, a notification, or a sharing change. Scans are completely transparent to them.
What happens when the 14-day trial ends?
The product switches to read-only mode. Historical findings and reports stay visible so you can export them, but scheduled scans pause until you pick a paid plan. No credit-card surprise charge. You can revoke admin consent at any time and our scanner loses access immediately.
We're an MSP with multiple customer tenants – does that work?
Yes – see the MSP plan on the pricing page. Each customer tenant's data is kept strictly apart, and the database itself enforces that separation on every request; a single MSP console rolls up findings across tenants. Start with a free trial on one tenant first to get comfortable, then flip the switch.
What if the first scan finds a lot – doesn't that make me look bad?
The opposite – it's your budget request. Every first scan we have run so far found things – including in a well-run tenant whose admin writes his own PowerShell controls. That's the inheritance of Microsoft's defaults and every admin before you – not an audit of you. Most findings take minutes to fix once they're visible, and the dated report turns "we should do something about M365" into a concrete, costed cleanup plan you present on your own terms – before someone else asks the question for you.
We already have Defender, Purview and Secure Score. What does Cyber add?
The answer, not the settings. Microsoft's consoles are organised by product; Cyber is organised by question: who can reach what, since when, and who fixes it. Three things you will not get from the admin centre: a per-person and per-Team view of every membership, ownership and sharing link (the leaver check and the access review); a Secure Score read against the licences you actually own, so the target is reachable; and delegation – each Team owner sees only their own groups and their own to-do list. See "Doesn't Microsoft already do this?" above. It reads your tenant through Microsoft's own Graph API, read-only, and needs no P2 licence.
Can someone walk us through the first scan?
Yes – a 20-minute guided first scan. Bring the colleague who holds Global Admin (the consent is one click, by them), and you leave the call with your real findings list on screen. Book it here or write to contact@olyteck.com.

Your tenant has findings right now.

See who can open what before your next audit, your next storage invoice or your Copilot rollout, then hand the clean-up to the people who shared. 20 minutes with us, or 10 minutes on your own.

No credit card · All modules · Read-only · Cancel by doing nothing