CY Cyber — M365 Security
Microsoft 365 · access map · Teams campaigns

Who can open what in your Microsoft 365?

See it in minutes. Then let the people who shared it close it, right in Teams.

On the map: “Anyone” linksguests nobody remembersfolders still shared with a former contractorfiles open to the whole companylinks created by people who have left

A read-only scan shows who reaches which SharePoint sites, Teams and OneDrive files. Launch a campaign and each employee gets their own list in Teams. Every decision is dated and named, ready for your auditor.

  • Sign in with Microsoft
  • No credit card
  • Read-only scanner
  • Hosted in France
  • Counts, never files
Cyber in 80 seconds: why one admin cannot close a thousand shares, and who can.
Three situations you may have without knowing

Nobody decided it. It accumulated.

You inherited this tenant. It is not a fault. Your figures will be different. They will not be zero.

Copilot

Copilot breaks nothing. It finds what everyone can already open.

Files open to the whole company, to guests, or to anyone with the link: Copilot answers from all of it. Cleaning up before it is opened to everyone costs far less than after the first "how did you find that?".

A leaver

Disabling an account does not close its shares.

Badge returned, laptop returned, account disabled. Their OneDrive is still shared with two outside addresses, an "Anyone" link still opens the price list, and they still reach a dozen sites. No offboarding checklist has a box for that.

Storage

You may be paying for files nobody opens.

SharePoint storage beyond the included pool is billed every month. Inactive sites, leavers' OneDrives and forgotten archives fill it quietly. Cyber shows the biggest sites and drives, quotas over 90 % and what is safe to archive.

1 · See

The access map: who reaches what, in one picture.

Six views drawn from the scan you already ran: no extra Microsoft permission, no file opened. Each one answers a question an auditor or a director will ask you.

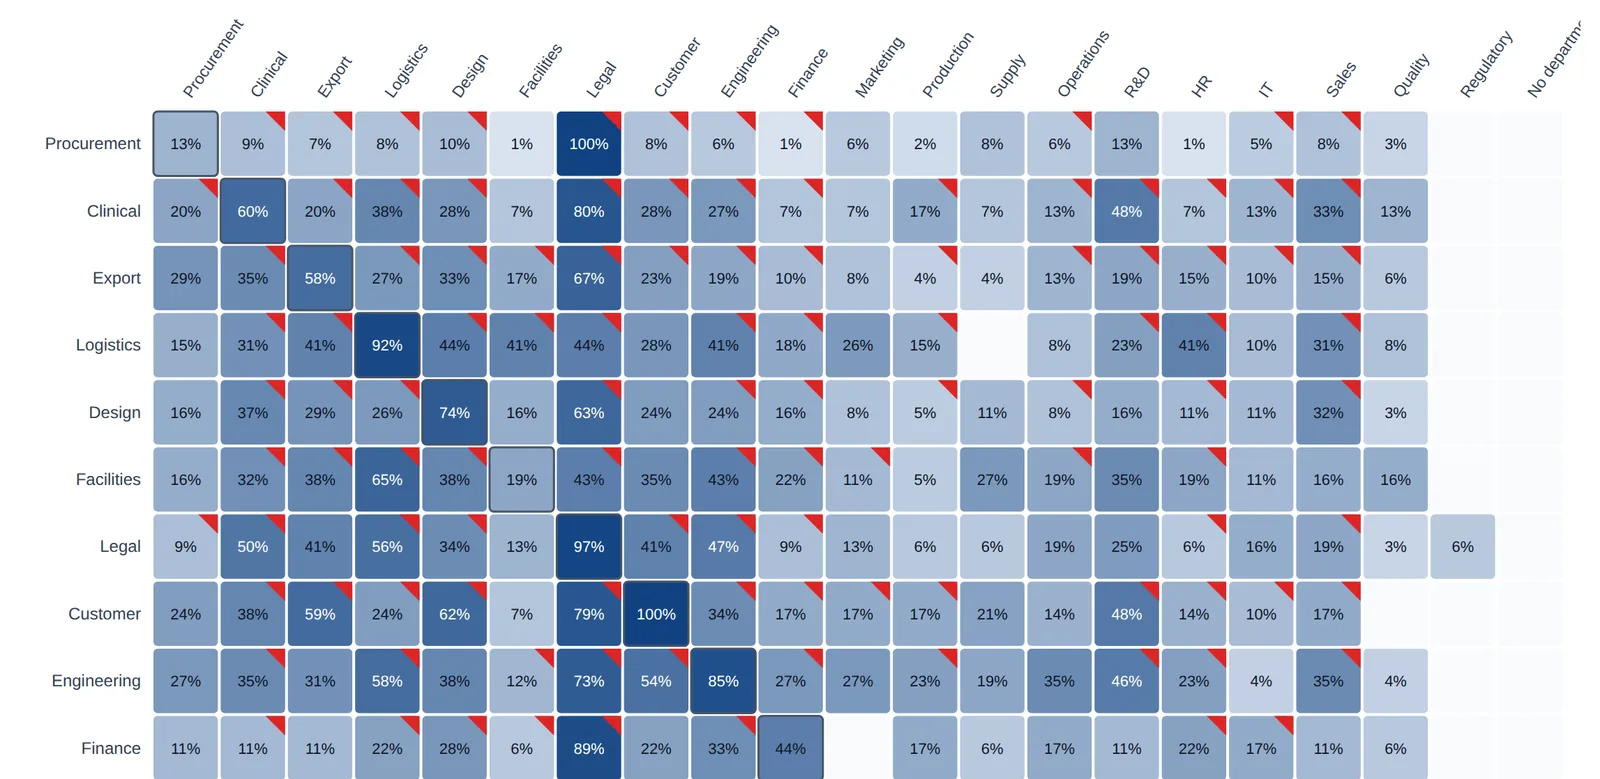
Access map heat grid: share of each department that can open the sites of every other department
Which departments open which departments' sites? Rows: the people of a department. Columns: the sites of a department. The diagonal is normal; the red corners nobody decided. One click on a cell lists the sites.
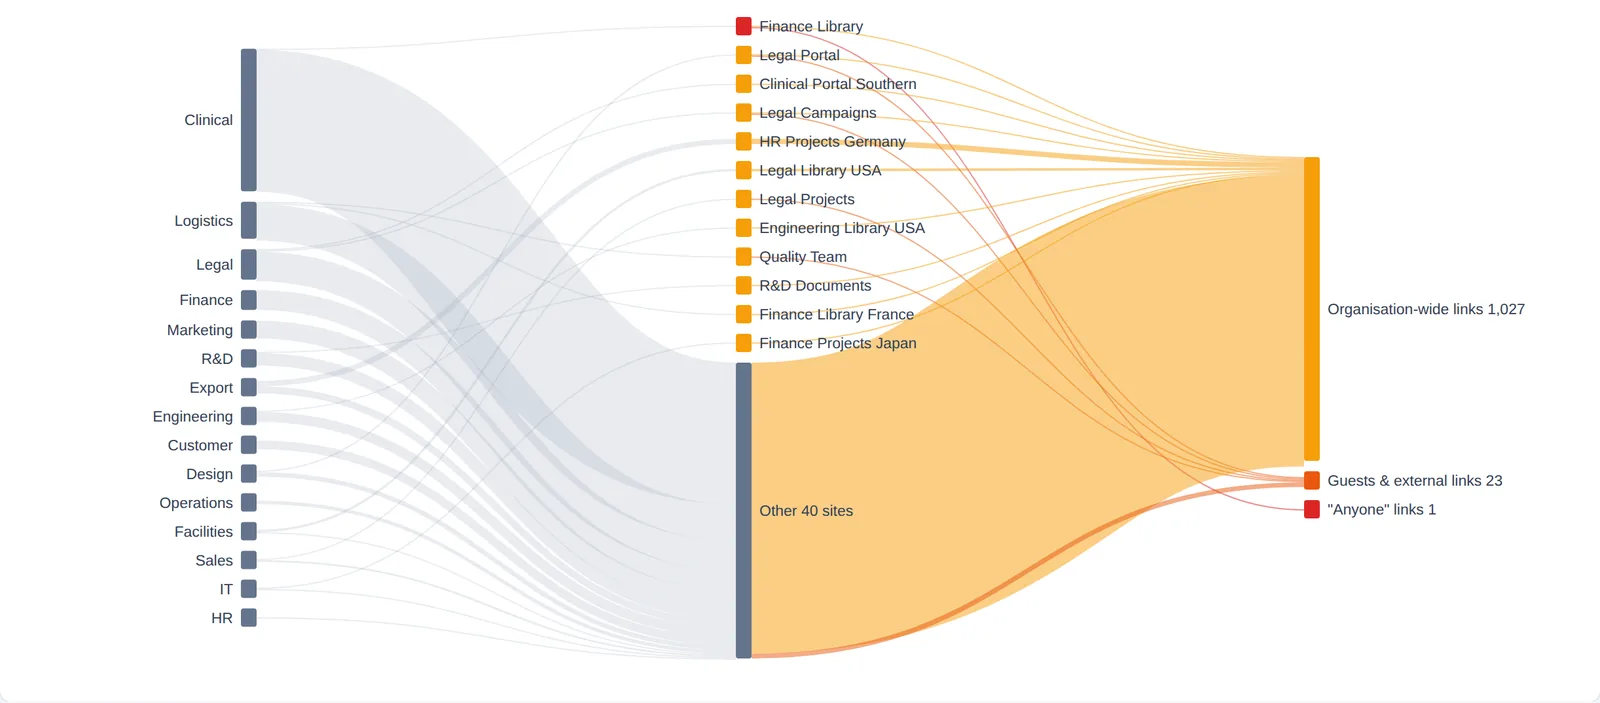
Flow from owning departments to sites to organisation-wide links, guests and Anyone links
Where does access leave the company? From the owning department to the sites, then to organisation-wide links, guests and "Anyone" links. The width of a flow is the number of accesses.
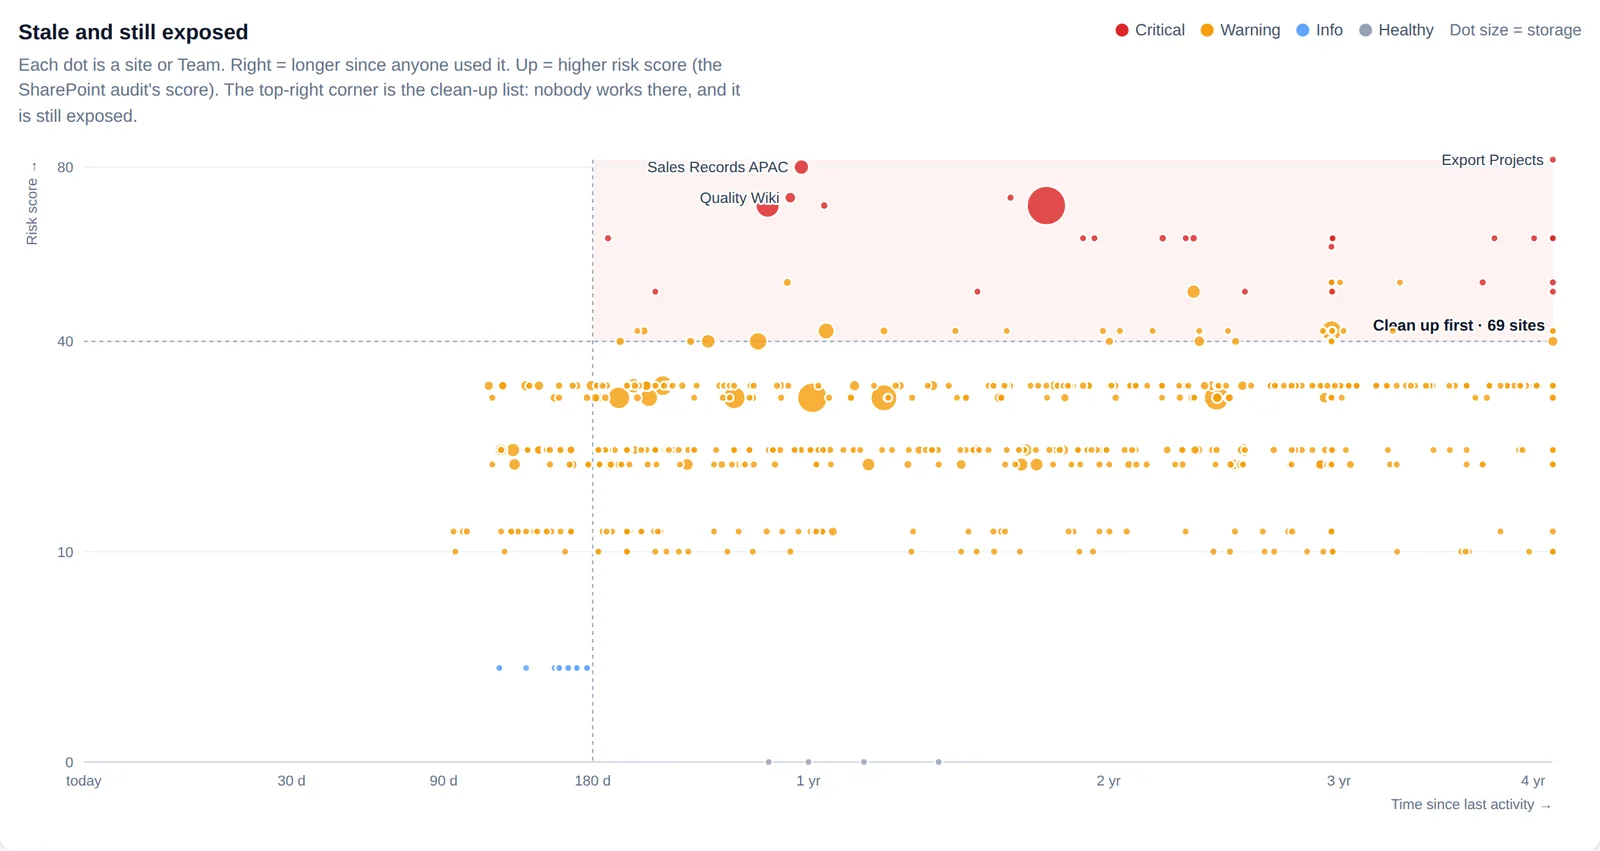
Scatter of sites by time since last activity and risk score; the top-right corner is the clean-up list
What is dead but still open? Each dot is a site or a Team. Right: unused for longer. Up: more exposed. The top-right corner is the clean-up list, already sorted.

Sites named like sensitive content (payroll, HR, contracts) are flagged for every department except their owner: without reading a file, without an E5 licence.

Typical situation · fictional tenant · real Olyteck Cyber screens

2 · Fix, without IT doing it

Each person closes what they shared. From Teams, in a few minutes.

Security cannot judge 40,000 files. The person who created the folder can. A campaign sends each owner their own list, and the fix happens on their own page: close the link, or confirm it is still needed.

1

You launch the campaign

Pick the sources (OneDrive, SharePoint and Teams sites), the link types, 14 to 35 days, the tone and the language. From then on, Olyteck sends, reminds and stops on its own.

2

They get it in Teams

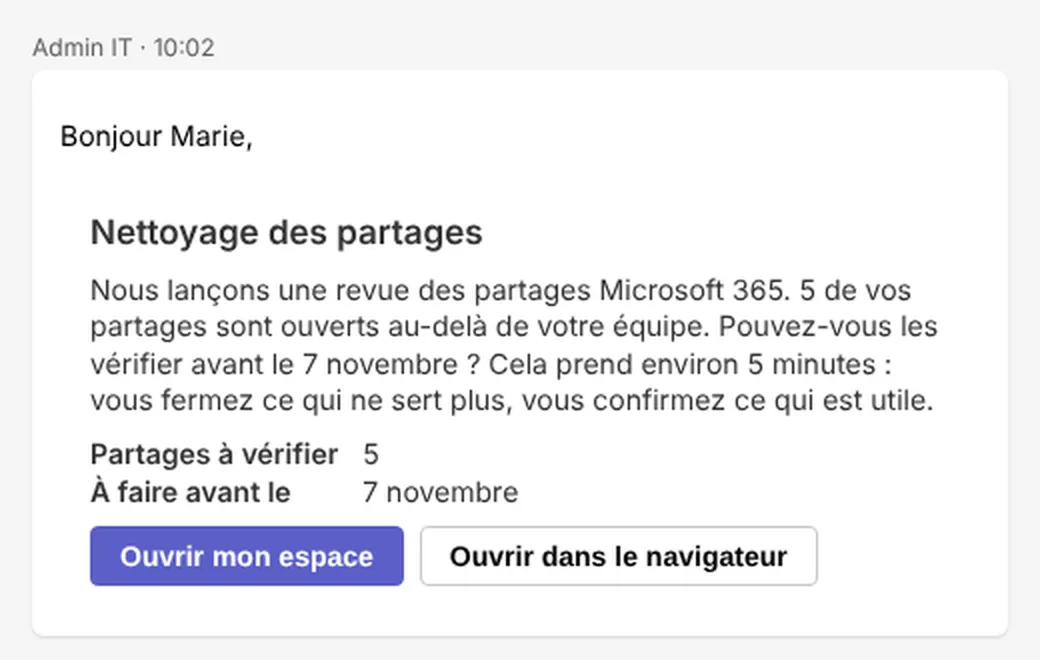
A notification in their activity feed and a direct message in their chat: how many shares to check, by when, one button. Reminders on working hours only, never once nothing is left.

3

They fix it in Mon espace

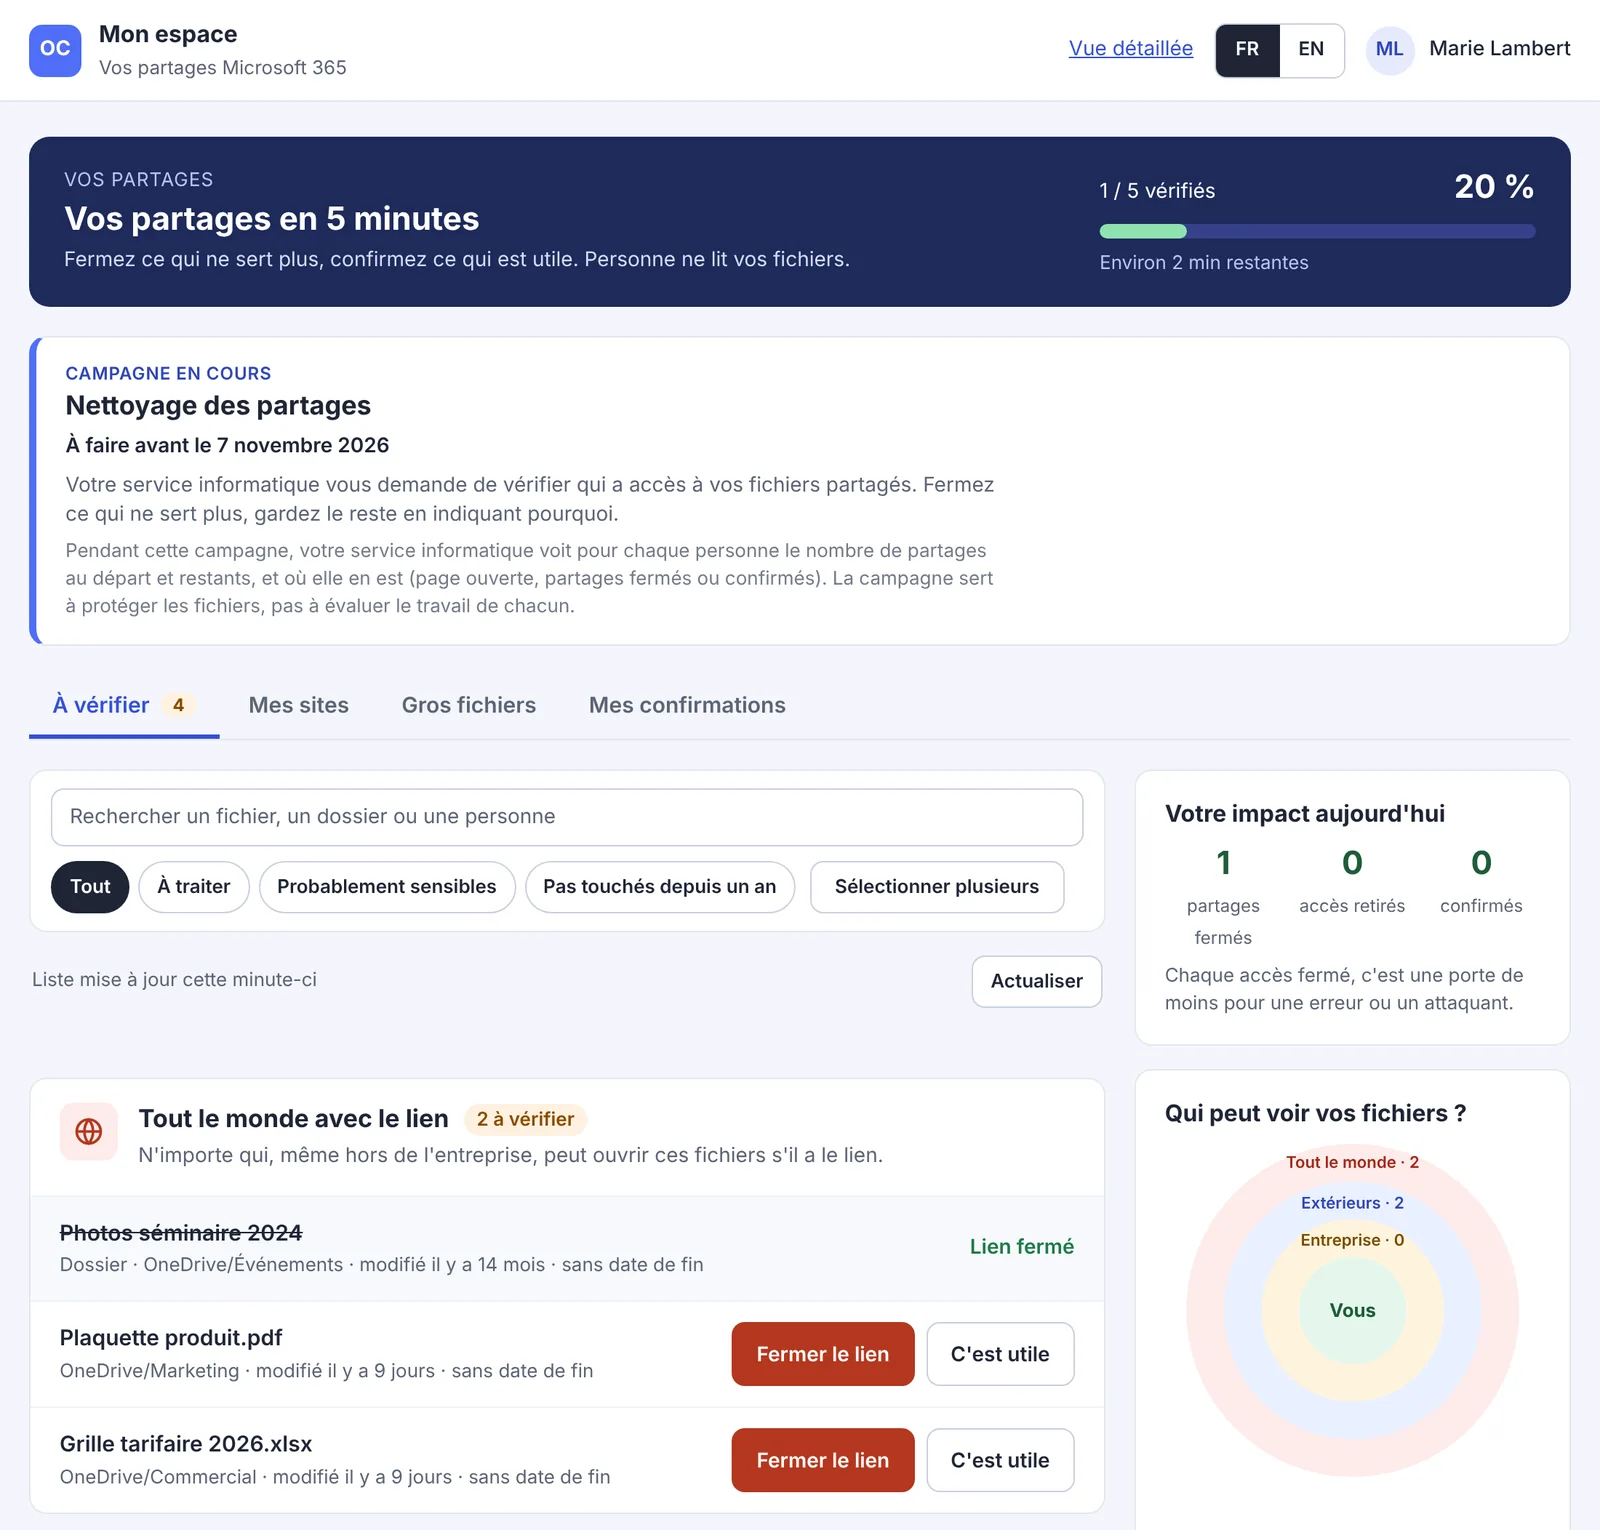
One number to bring down. Close or confirm each link in one click, inside Teams, with their own Microsoft rights. The page says plainly what IT can see.

Teams chat card: Nettoyage des partages, 5 shares to check before 7 November, button Ouvrir mon espace
The direct message in Teams chat, "classic" tone

Everything happens in Teams

The notification rings in their activity feed, the message lands in their chat, and Mon espace opens inside Teams. No link to copy, no unknown website, no extra password: it is the tool they already have open, so that is where they fix. Simple for them, more shares closed for you.

  • Activity-feed notification
  • Direct chat message with buttons
  • Mon espace as a Teams tab, signed in by Teams
Mon espace: progress 1 of 5 checked, the running campaign and what IT sees, links to close or keep, who can see your files
Mon espace: what the employee sees Their progress, the campaign and its deadline, what IT can and cannot see, then each link with "Close the link" or "It's useful".

Three tones

Classic, friendly or playful: you pick the voice of the messages for each campaign.

We run it, IT watches the results

Olyteck sends the messages, reminds at the right moment and stops when there is nothing left. IT: three steps once, a campaign in a few clicks, then the live follow-up. No ticket, no script, no chasing.

Typical situation · fictional tenant · real Olyteck Cyber screens

3 · Prove

The trace your auditor asks for is built while you work.

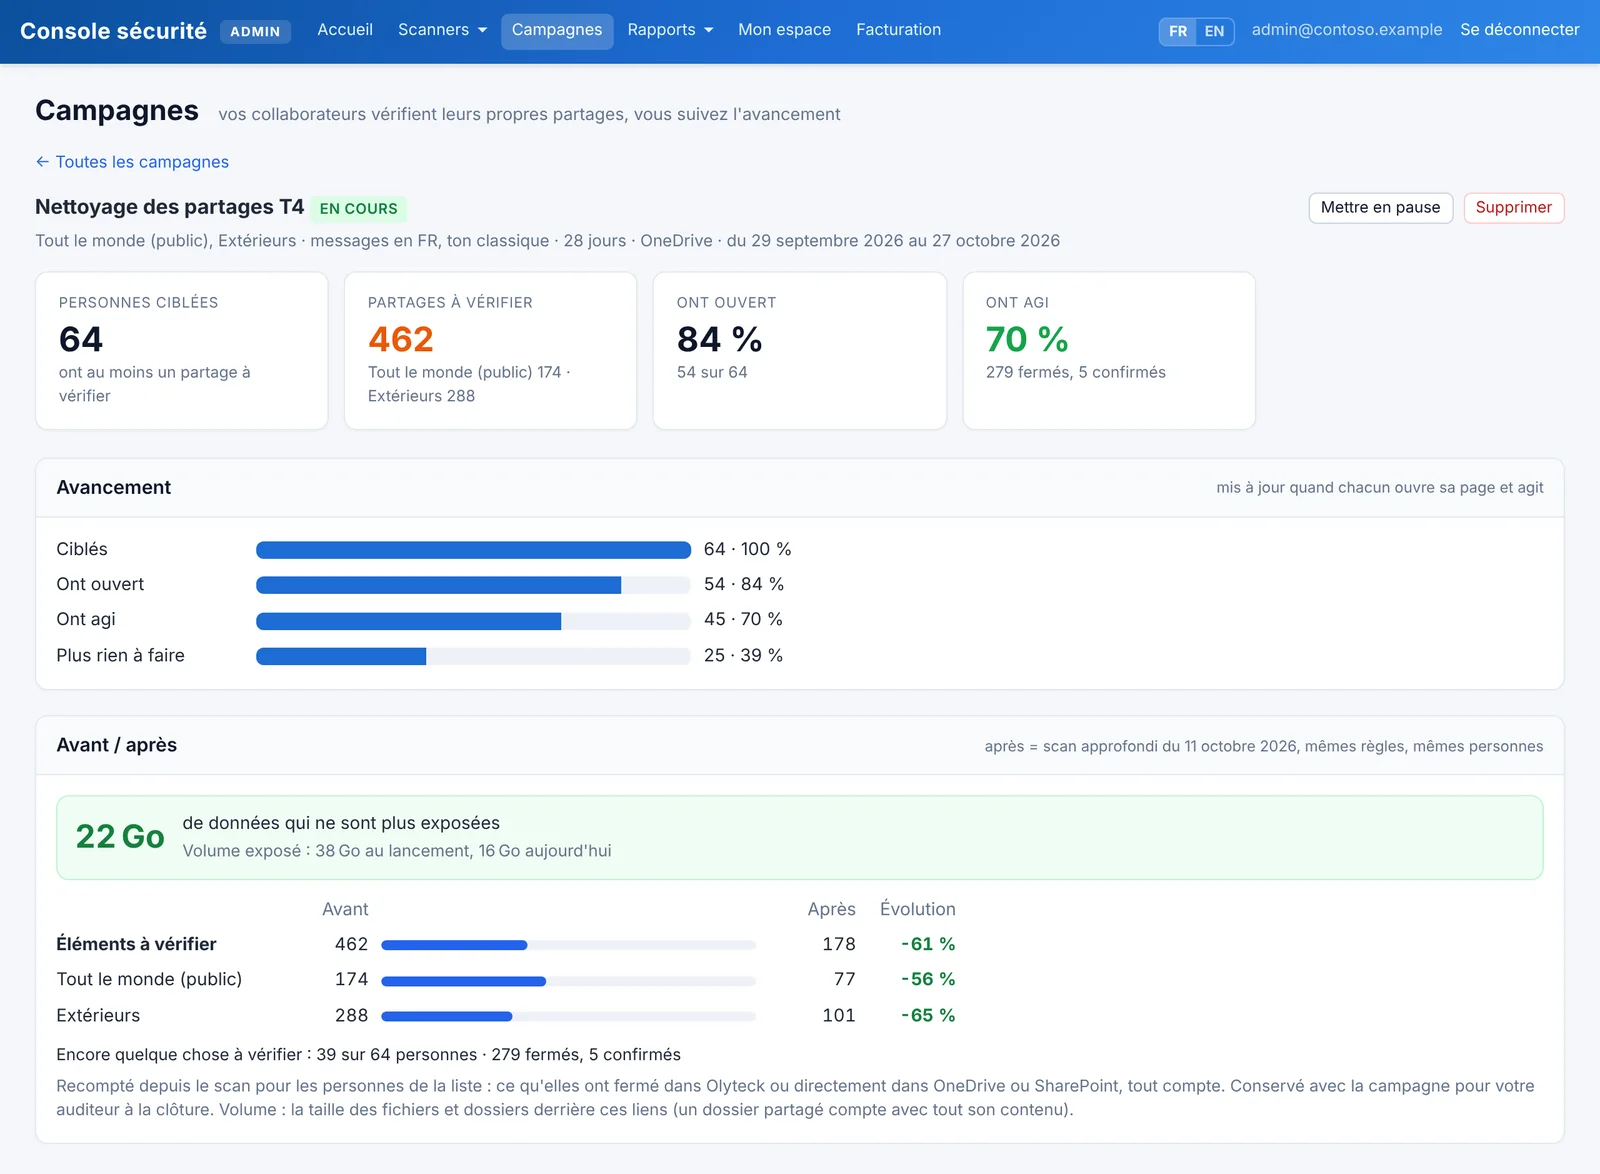
A running campaign in the console: people targeted, shares to check, opened, acted, progress bars and the before / after
What IT sees: who opened, who acted, and the before / after "After" is a new deep scan with the same rules and the same people. It is kept with the campaign for your auditor at close. Figures of a fictional tenant.

The campaign funnel

Targeted, opened, acted, nothing left to do: per campaign and per department, with the before / after and a CSV export.

Dated, named decisions

Every accepted access carries a name, a date and a reason, and comes back for review after 12 months. Every fix lands in the audit trail and in your own Microsoft audit log.

Your access review

ISO 27001 calls it an access review (A.5.15, A.5.18); NIS2 Article 21 asks for access control. The map, the decisions and the funnel are the evidence.

Live in under 10 minutes

Three steps to your map. A fourth, when you decide, to fix it.

From "I just heard about this tool" to "here is who can open what" — typically under 10 minutes to the first results on a standard tenant.

1

Sign in with Microsoft

Standard Microsoft SSO. PKCE, delegated scopes. We never see your password. Takes ~30 seconds.

~30 seconds
2

Grant read-only admin consent

One click by a tenant admin. 19 read-only Graph permissions. You can revoke consent at any time from the Microsoft admin centre and the scanner stops cold.

1 click
3

Deep scans run on our servers

Started for you, in France, with no browser left open. First results in minutes; a large tenant completes in the background. Then every 7, 14 or 30 days, or on demand.

Minutes, then background
4

Fixing and campaigns — when you decide

Fixing is a separate application with its own consent: it acts as the person clicking and lands in your own Microsoft audit log. Teams messages use a third application that can read nothing: approve it, upload the Olyteck Teams app, send a test. Never enable them and the product stays read-only forever.

Optional · separate consents
What we never store

Your files never leave your tenant.

Most scanners ingest the content. Cyber — M365 Security doesn't. Here are the three classes of data we deliberately do not pull or persist.

✕ File contents

We don't read what's inside your files.

No document bodies, no attachments, no OCR text. The scanner identifies that a file is shared, never what is inside it. Your IP and customer data never enter our database.

✕ Share URLs

We record that a share exists — not the link.

When a SharePoint site has an "Anyone" link, we store the count and severity. We do not store the URL itself. Rogue links can't leak from our database because we never asked for them.

✕ Scanner access tokens

Scanner tokens live in memory for one scan — then are gone.

The scanner's access tokens are held in memory for the lifetime of a single scan and discarded. The optional fixing and Teams chat connections keep a refresh token, encrypted (AES-256-GCM) with a key that is not in the database, and delete it when you disconnect them in Cyber (revoking the app in Microsoft makes it useless). A database dump of Cyber — M365 Security alone cannot be replayed against your tenant.

Four Microsoft applications, each with one right

Separate apps, separate consents, each one revocable on its own. You can check every grant in Entra under Enterprise applications.

Sign-inIdentifies the person through Microsoft. Nothing else.
Scanner19 read-only permissions. Reads, never writes.
Fixing · optionalCloses a link or removes a member, as the person clicking, with their rights.
Messaging · optionalSends Teams notifications to people who have the Olyteck app. Reads nothing.

Employees involved? Built by a DPO. We give you the CSE information notice and the IT-charter clause. The campaign list (name, e-mail, department, counts, events) is deleted 90 days after the campaign closes. No ranking of people, no file names, no links kept.

The full SAFE-payload rule is codified in our Privacy Policy §3.

Read-only by default Scanner never mutates your tenant unless you explicitly invoke it.
Hosted in the EU Application data stays in the European Union. GDPR-aligned.
SAFE payload Counts & IDs only — never file contents.
No scanner tokens stored They live in memory for one scan. Optional connections keep an encrypted, revocable token.

Built for the security admin who has 20 other things to do.

Short path from "is this a risk?" to "here's the evidence."

Deploys in 10 minutes

Sign in with Microsoft, grant admin consent, finish the 4-step wizard. Your first scan runs automatically. No agents to install, no firewall rules, no ticket to IT.

SSO + admin consent + wizard

Executive-ready reports

Snapshot any scan to a saved report: cover page, trend chart, top findings, auditable timestamp. Share externally via a signed URL that expires on your schedule. No re-query, no PowerPoint night.

Saved reports · signed share URLs

Weekly digest + critical alerts

Monday-morning summary of new, resolved, and outstanding findings — sent in your tenant's local timezone. Critical findings page you immediately. Admins can opt out per-module.

Tenant-local digest · per-module opt-out
The objection, weighed

Which is riskier — a read-only scan, or not knowing?

Starting the trial

  • Ten minutes, read-only Graph scopes — nothing in your tenant changes
  • No credit card, no agents, no firewall rules, no IT ticket
  • Consent revocable in one click from your Microsoft admin centre — the scanner stops cold
  • Worst case: you spent ten minutes confirming your tenant is clean

Doing nothing

  • The anonymous links stay live — unlogged, unexpiring, unwatched
  • Ex-employee OneDrives keep holding data nobody is responsible for
  • Vendor guests keep Owner rights; consented OAuth apps keep mailbox access
  • Worst case: your auditor, your insurer, or an attacker finds it before you do

Not looking doesn't make the findings go away. It just guarantees you're the last to know about them.

The first question every admin asks

"Doesn't Microsoft already do this?"

It shows you settings. Site by site, page by page, across four admin centres that get renamed every year. What it doesn't give a small team is the answer: who can reach what, since when, and what to do about it.

Admin centre: settings

Cyber: consequences, per person, per Team, per link

Pick one person and see every Team, site and sharing link they hold — the leaver check in one filter. Pick one Team and see what is open internally, to guests, or to anyone on the internet. Close it in one click. That is the access review an auditor asks for, done in minutes instead of a week of PowerShell.

Microsoft: four consoles that keep moving

Cyber: one checklist of best practices that stays put

Entra, Purview, Defender, SharePoint admin — tools get renamed, pages move, the guidance is scattered. Cyber keeps the controls that matter in one place, in ISO 27001 and NIS2 vocabulary, readable by an IT team that doesn't have a Microsoft security specialist on staff.

Secure Score: a target you can't reach

Cyber: the score achievable on the licences you pay for

Half the recommendations need a P2 licence you don't have, so 100 % is off the table and the number stops meaning anything. Cyber shows the maximum achievable on your current licences, the points you can win today, and what an upgrade would actually unlock — before you buy it.

Admin centre: one global admin does everything

Cyber: the clean-up goes to the people who shared

Each owner gets their own list in Teams and works through it in Mon espace, with their own rights. You keep the overview and the proof; nobody gets admin rights.

Microsoft shows you the problem. Fixing it stays IT's job. Here, everyone fixes what they shared. Cyber reads your tenant through Microsoft's own read-only Graph permissions and works on Business Basic, Standard and Premium. No P2 required.

What an evaluator said
"Achieving the same level of visibility using native Microsoft capabilities alone can be difficult or, in some cases, not possible."
A corporate security lead at an IT services company, during a formal vendor evaluation of Cyber

14-day free trial — the full product, no card.

First results in minutes, every module unlocked, cancel by doing nothing. Send yourself or a colleague a test campaign message in Teams before you decide.

  • All 7 modules + access map
  • Deep scans on our servers
  • Mon espace + Teams messages
  • 20 on-demand scans / day
  • Weekly digest + critical alerts
  • Read-only by default · Hosted in France

A pilot campaign on one department needs more than 14 days? Write to us, we extend the trial.

Start the free scan →

Simple pricing. No surprise paywall.

Three editions, priced by licensed users (up to 100, 300, 600 or 1,000). Your 14-day trial unlocks everything. Annual billing is 2 months free; monthly has no lock-in.

Voir

See who can open what: access map, risks and reports.
from €99/mo
billed annually · up to 100 users, then by size
  • 5 modules included
  • Daily scheduled scans
  • Access map and admin reports
  • 90-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial
Most popular

Corriger

Owners fix their own shares from Teams. IT watches the results.
from €199/mo
billed annually · up to 100 users, then by size
  • 6 modules included
  • Daily scheduled scans
  • Clean-up campaigns in Teams + Mon espace
  • 180-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial

Piloter

All seven modules, unlimited scans, a year of history.
from €299/mo
billed annually · up to 100 users, then by size
  • All 7 security modules
  • Daily scheduled scans
  • Clean-up campaigns in Teams + Mon espace
  • 360-day history
  • Weekly digest + critical alerts
  • Saved executive reports
Start free trial

Prices for every size, MSP and Enterprise on the pricing page.

One clean-up, no subscription

The clean-up campaign pack

For a first campaign, before a Copilot rollout, or for a budget line this year: 45 days of Cyber with campaigns, then you decide.

One-off price, licensed Microsoft 365 users, VAT not applicable (art. 293 B du CGI). Over 1,000 users: on quote.

Order a campaign →

Paid by card? We activate your 45 days within one working day and send you the kit.

Scan #1 · value in minutes

Here's what a typical first scan actually surfaces.

Not a marketing mock-up — this is the finding shape produced by the live SharePoint and OneDrive scanners on a real 50-seat tenant.

Critical
5 anonymous links on site "Client-X-Shared"
Oldest link created 2022-03-14. No expiry. Default sharing link set to "Anyone".
Warning
OneDrive for alex@acme.com — 312 GB
User licence revoked 2025-11. Account disabled. Drive still holds 312 GB.
Info
Leaver check: 1 person → 14 Teams, 3 sites owned alone, 9 live share links
Person view before the exit interview: every group membership, every site they own alone, every link they created — including the ones shared to their private address. Remove or revoke from one screen; export the rest as the offboarding checklist.
Critical
External guest holds Owner on 4 team sites
partners@vendor.com — last sign-in 2025-09. Still Owner on Finance-Q4, Legal, HR-Docs, Ops.
Show 7 more findings from the same scan
Warning
7 sites above 90% quota · top site 4.2 TB
"Marketing-Archive" at 4.2 TB / 4.5 TB. Projected full in 6 weeks at current growth.
Warning
8 OAuth apps with Mail.ReadWrite · 3 inactive
Three apps not seen in tenant sign-in logs > 90 days. Still consented. Safe to revoke.
Critical
Team "Project-Phoenix" is Public — 412 users can read M&A channel
Visibility set to Public on creation. All org-wide licensed users can join, read channels, and download files — including the M&A-Q4 channel.
Warning
47 Teams have no owner · 8 inactive > 180 days
Original owners offboarded. Nobody can approve new members or archive. Export the list and flag them for archive.
Info
23 M365 Groups eligible for archive · 1.8 TB reclaim
Zero activity > 180 days. No guests. Safe archive candidates. Add to the Archive Queue and export the report for your ops team.
Critical
"Anyone with the link" default is tenant-wide
Org-level default sharing scope is still "Anyone". Every new link inherits it.
Info
3 admins without MFA enforced
Global Admin + SharePoint Admin + Exchange Admin. Conditional access not requiring second factor.

Every finding exports to CSV, links back to the exact SharePoint/OneDrive object, is timestamped for auditor evidence — and has a fix button next to it: revoke the link, remove the member or guest, demote the owner. Read-only until you say otherwise. Run your own scan →

And the rest of the scan

Security, hygiene and storage: the same scan, three answers.

Every read-only scan doubles as a security audit, an asset-hygiene report, and a storage-cost exercise. You pay for one tool and three different people on your team stop complaining.

Security posture

Find the things an attacker — or your auditor — would find first.

  • Anonymous "anyone-with-the-link" shares (no expiry, no audit)
  • External guests holding Owner / admin rights on sites & Teams
  • Public Teams & channels exposing confidential data org-wide
  • OAuth apps with mail, Files.ReadWrite or Sites.FullControl scopes
  • MFA gaps, legacy auth, conditional-access posture drift
  • Copilot blast radius — dormant licences and the oversharing Copilot will surface on rollout

Asset hygiene

Find the zombies. Ownerless Teams, abandoned Groups, OneDrives of disabled users, sites nobody opens.

  • Ownerless Teams & M365 Groups — no one left to review access
  • Abandoned Teams with zero activity > 180 days — archive candidates
  • OneDrives for disabled or unlicensed users (cleanup candidates)
  • SharePoint sites inactive > 90 days with data still inside
  • Guest accounts with no sign-in activity in last N days
  • Teams with external members added months ago, never removed

Storage & cost

Answer "why is the M365 bill climbing?" in a meeting, not a week.

  • Top-N storage hog sites & OneDrives with exact GB & allocation %
  • Quotas > 90% — before Microsoft throttles your users
  • GB-per-disabled-user — the clean-up-and-save-money list
  • Sites over configurable threshold (default 50 GB) flagged
  • Per-tenant storage trend, week over week

SharePoint & OneDrive are the "most used" modules for a reason — one scan feeds all three outcomes. Every Team has a backing SharePoint site, so Teams, Groups, channels (including Public vs Private visibility), ownership, and activity are all enumerated in the same pass — with a one-click Archive Queue for the cleanup list.

Four questions

Could you answer these in a meeting — today?

Your ISO 27001 auditor calls it an access review. Your cyber-insurer and your biggest customer's security questionnaire ask versions of the same four questions. "I'd have to check" is the answer that costs deals, premiums, and audit findings.

1 How many "Anyone with the link" shares exist in your tenant right now?
2 How many OneDrives of people who left still hold company data — and how many GB?
3 Which Teams have external guests in them, and who approved each one?
4 Which third-party OAuth apps can read your mailboxes today?

If any answer is "I'd have to check" — that check is the free trial. Ten minutes, read-only, and you'll have all four answers with timestamps. Not knowing isn't neutral: it's the same exposure, minus the chance to fix it first.

Get the four answers →
Why now, not next quarter

Two reasons not to wait, and one already in force.

Tenant hygiene has been postponable for years. Copilot ends that, NIS2 will, and GDPR already did.

Now

Copilot answers from what people can open.

Copilot reads everything each user can read. Every overshared file of the last years is one question away. Cleaning up before it is opened to everyone costs far less than after the first "how did you find that?".

Pending in France

NIS2: the French law is coming, the measures are known.

France's Résilience bill, which transposes NIS2, is still before Parliament with no date set, while most other EU states have already transposed it. Article 21 already says what to show: access control and asset management. A dated access review today is a head start, made without enforcement pressure.

Already in force

Regulators punish negligence, not breaches.

GDPR Article 32 requires demonstrable security measures — incident or not. Recent CNIL sanctions repeatedly cite "letting structural problems persist". A timestamped quarterly report is the difference between negligence and diligence on file.

Need something to show your management first? Ask for an anonymized sample executive report: contact@olyteck.com

Common questions

What every IT lead asks before the first scan.

Will my employees think the Teams message is phishing?
It comes from inside your tenant. The message is sent by the Olyteck app your admin installed in your own Teams, it opens a page signed in with Microsoft, and it never asks for anything but the usual Microsoft sign-in. Before launch, announce the campaign from your own management: we give you the text, to be signed by your IT and security leads. No e-mail from an unknown domain asking staff to "fix their shares".
Do we have to inform the works council (CSE)?
In France, usually yes, and we make it easy. A campaign shows each employee their own shares: that is processing of employee data. We give you the CSE information notice and the IT-charter clause. What we keep is minimal: name, e-mail, department, counts and campaign events, deleted 90 days after the campaign closes. No ranking of people, no file names, no links.
What if people don't fix anything?
Expect a minority to do most of the work, and that is enough. Exposure usually sits with a few owners, so the people who act close most of the risk. Reminders stop as soon as someone has nothing left. What remains at the end, IT closes from the console, one click per link.
How long does a campaign take, and how much IT time?
14 to 35 days, chosen at launch. A campaign starts from a deep scan of 7 days or less (one click: "Run now"). Then messages go out on their own, Monday to Friday, 8:30 to 18:30 in your tenant's time zone. IT time: the launch, a look at the funnel, and the remainder at the end.
Is the scanner really read-only? Can it change anything in my tenant?
Yes — and it is not a setting, it is the permission grant. The scanner application holds 19 Microsoft Graph permissions and every one of them is read-only. It has no write permission of any kind, so there is no code path by which a scan can modify your tenant. It is also the only identity that reads your tenant on a schedule, so nothing on a timer can change a file, site, group or setting (the only other scheduled action is sending the Teams reminders of a campaign you launched).

Fixing what we find is a separate application, and it is optional. Revoking a sharing link or removing a group member needs its own Entra registration, consented separately and revocable on its own. If you never enable it, the product cannot modify your tenant at all — every fix button refuses and tells you which permission it would need. When you do enable it, it acts as the person clicking, with that person's own rights, and the action appears in your own Microsoft audit log.

Don't take our word for it: check Enterprise applications → Permissions in your own tenant, or Security Console → Apps & consent in the product, which reads the live grant from Microsoft on every load. Security review brief (PDF) →
What data do you actually store in your database?
Counts, IDs, and severities — not content. For each finding we store the site, person or app it is about (ID and name), the finding type, the severity, and the timestamp. We do not store file contents, share URLs or email bodies, and the scanner's access tokens are never stored. Two exceptions, both about one person's own choices: a share an employee confirms in My space keeps the file name and their reason, and a fix waiting for an approval keeps its file name for up to 30 minutes. The optional fixing and Teams chat connections keep an encrypted refresh token. See Privacy §3 "SAFE payload" for the precise field list. Database is hosted in the EU. Scan history is available and kept for 90, 180 or 360 days depending on your plan (Voir, Corriger, Piloter; Enterprise: as agreed), then deleted; a resolved finding is deleted 180 days after it was resolved (360 on Piloter).
Do I really not need a credit card to start?
Correct. Sign in with Microsoft, grant admin consent, and you're in. The 14-day free trial unlocks all 7 modules — SharePoint, OneDrive, Copilot, Identity, Email security, OAuth apps, Posture — with daily scheduled scans, weekly digest, critical alerts, and saved reports. Nothing rolls over to a paid plan automatically. When the trial ends, the product switches to read-only until you pick a plan.
How long does a scan actually take?
5–15 minutes for most SMB tenants. Heavily-loaded tenants (500+ SharePoint sites) can run longer. The scanner is rate-limited to respect Microsoft Graph throttling and always yields to your users — no impact on production. You can run up to 20 on-demand scans per day during the trial.
Can I share findings with my accountant or external auditor?
Yes. Any scan can be snapshotted to a saved executive report — cover page, trend chart, top findings, auditable timestamp. Share externally via a signed URL with your own expiry, or export findings as CSV for evidence attachments. No re-query needed from the auditor's side.
Will this disrupt my users during a scan?
No end-user impact. All calls go to Microsoft Graph application endpoints using the tenant's own admin consent — not to users' mailboxes or OneDrives. Users won't see a prompt, a notification, or a sharing change. Scans are completely transparent to them.
What happens when the 14-day trial ends?
The product switches to read-only mode. Historical findings and reports stay visible so you can export them, but scheduled scans pause until you pick a paid plan. No credit-card surprise charge. You can revoke admin consent at any time and our scanner loses access immediately.
We're an MSP with multiple customer tenants — does that work?
Yes — see the MSP plan on the pricing page. Each customer tenant gets its own isolated scan database; a single MSP console rolls up findings across tenants. Start with a free trial on one tenant first to get comfortable, then flip the switch.
What if the first scan finds a lot — doesn't that make me look bad?
The opposite — it's your budget request. Every first scan we have run so far found things — including in a well-run tenant whose admin writes his own PowerShell controls. That's the inheritance of Microsoft's defaults and every admin before you — not an audit of you. Most findings take minutes to fix once they're visible, and the dated report turns "we should do something about M365" into a concrete, costed cleanup plan you present on your own terms — before someone else asks the question for you.
We already have Defender, Purview and Secure Score. What does Cyber add?
The answer, not the settings. Microsoft's consoles are organised by product; Cyber is organised by question: who can reach what, since when, and who fixes it. Three things you will not get from the admin centre: a per-person and per-Team view of every membership, ownership and sharing link (the leaver check and the access review); a Secure Score read against the licences you actually own, so the target is reachable; and delegation — each Team owner sees only their own groups and their own to-do list. See "Doesn't Microsoft already do this?" above. It reads your tenant through Microsoft's own Graph API, read-only, and needs no P2 licence.
Can someone walk us through the first scan?
Yes — a 20-minute guided first scan. Bring the colleague who holds Global Admin (the consent is one click, by them), and you leave the call with your real findings list on screen. Write to contact@olyteck.com and we'll set it up.
Your tenant has findings right now.

See who can open what before your next audit, your next storage invoice or your Copilot rollout, then hand the clean-up to the people who shared. 10 minutes, no card, Microsoft sign-in.

Start the free scan → No credit card · All modules · Read-only · Cancel by doing nothing

Prefer a guided first scan? 20 minutes, bring your Global Admin — contact@olyteck.com

About cookies on this site

We'd like your permission to use optional audience-measurement cookies — they help us understand which pages work and which don't, so we can improve them. Decline and the site stays free of analytics cookies. See the Cookie Policy for the full list of cookies, their purpose and lifetime.

Your choice is saved for 6 months on this device.